Key takeaway
Define which system owns each field, preserve stable source identifiers, and test replays, late changes, and records that cannot be matched.
Connecting a CRM to reporting can remove exports, but it can also automate ambiguity. Two contacts may represent one person. A status may change after the cutoff. One system may own an address while another owns the billing relationship. A reliable integration makes those boundaries explicit rather than assuming that moving records makes them consistent.
Create a field ownership and identity map
For each important field, record its authoritative system, stable identifier, target meaning, and approved update rule. Decide whether this is read-only reporting or whether it writes back into an application. Those are different scopes with different risks.
Do not treat email alone as a permanent universal person identifier. Addresses can change, be shared, or be absent. Preserve source record IDs and define a reviewed matching process for records that must be combined. Keep ambiguous matches visible instead of silently forcing an identity.
Design for updates, deletions, and late records
An initial load is only one state of the pipeline. Determine how later changes are discovered, how deleted or archived records appear, and whether the API supports the required history. Read that vendor's documentation before selecting a polling or event-based approach.
Use an illustrative test: a case arrives Tuesday but is backdated to Monday, then its owner changes Wednesday. Should reporting reflect current ownership or ownership at the event? Define checkpoints so an interrupted load resumes without skipping the late record.
Make retries deliberate and repeatable
A transient failure may justify a retry; an invalid record or permanent permission failure needs another response. Microsoft's retry pattern guidance addresses retry policies and whether repeating an operation is safe.
A timeout does not prove a write failed. For write integrations, design an idempotency strategy and replay the same event in testing. PostgreSQL's INSERT documentation describes conflict handling that can contribute to database-side design. It does not, by itself, make every notification or external action idempotent.
Reconcile the source with the published output
Track extraction coverage, accepted records, failed records, and the reporting period that is complete. Compare agreed source slices with output. A successful API response can coexist with an integration that misses another page of results or unintentionally excludes a category.
Keep source references and transformation versions to trace published values. Monitor unexpected volume drops, new categories, and checkpoints that stop advancing. Alerts should identify the affected source, impact, and owner without exposing sensitive records or credentials.
Test recovery and document the operating boundary
Test an interrupted batch, duplicate event, late update, unmatched identifier, and approved credential-change procedure in a suitable environment. Define correction and reprocessing. Record business acceptance after recovery.
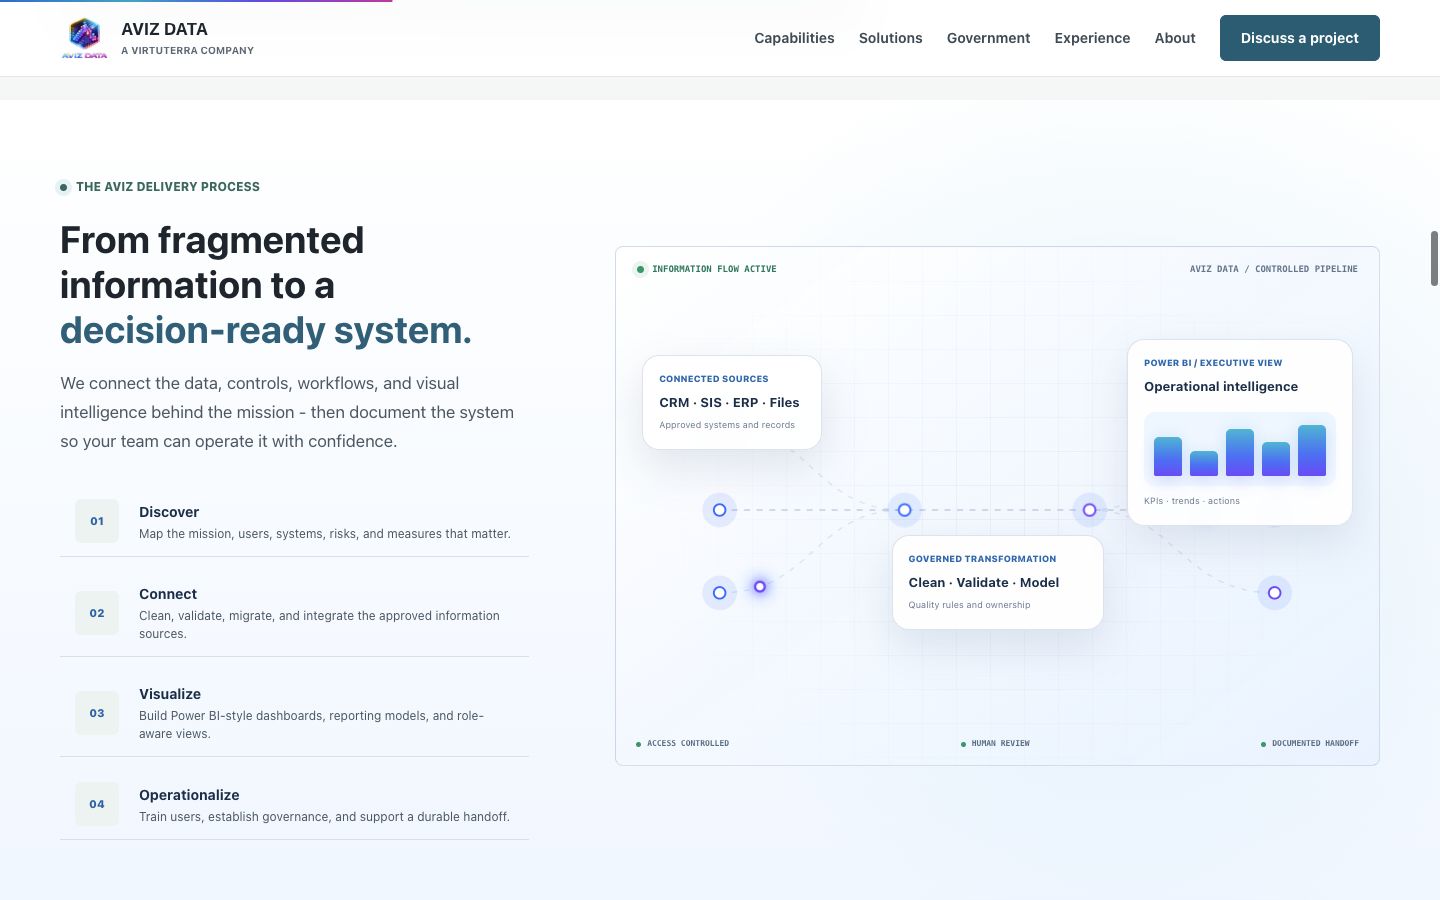
AVIZ DATA's API / Systems Integration and CRM / LMS Workflow Integration services offer starting scopes with explicit ownership and acceptance checks. For a transition, combine this work with the migration checklist and enterprise program planning.
Project checklist
- Source identifiers and field ownership preserved
- Read-only versus write-back scope agreed
- Updates, deletions, and late records handled
- Replay and retry behavior tested
- Reconciliation and exception ownership documented
References
- Microsoft Azure Architecture Center: Retry pattern
- PostgreSQL documentation: INSERT and conflict handling
AI-assisted guide checked against the linked platform documentation. Examples are illustrative and are not client results. Platform capabilities can change; confirm the requirements for your environment.